

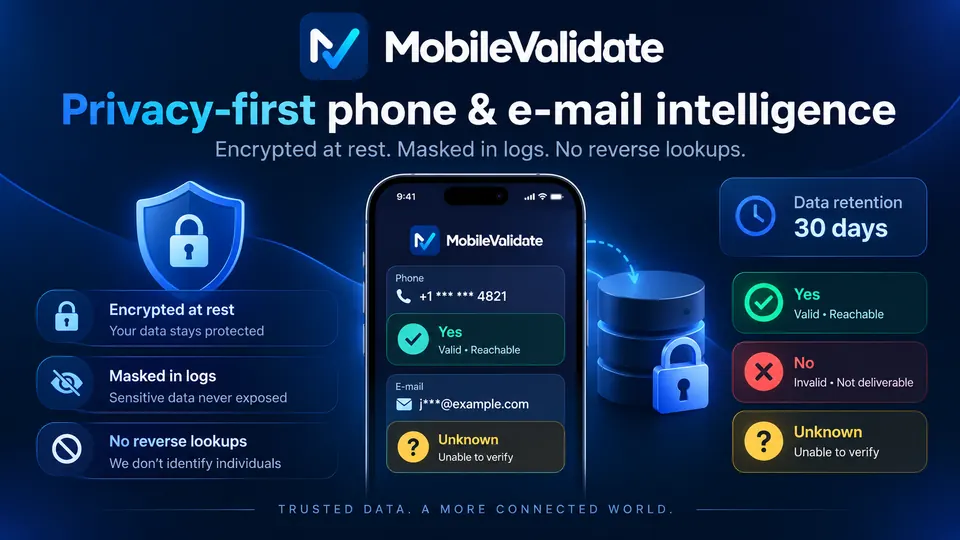
Phone numbers and e-mail addresses are personal data, and we handle them that way. Identifiers are encrypted when stored and masked wherever people see them. They are kept only for short default periods, and your cache is never shared with other customers. Anyone can object to being checked. This page describes these controls in plain terms. It is not a certification.
What is MobileValidate for?
MobileValidate exists to fight spam, fraud and abuse, and to make legitimate messages arrive. Businesses, carriers and messaging providers use it to screen sign-ups and one-time-passcode requests, clean contact data, pick a channel a contact can receive, and screen calls against spam reports.
- No reverse lookups. A check answers a narrow question about a number or address you already hold. It never returns names, photos, profiles, messages or locations.
- No enumeration. Sequential number ranges and generated e-mail lists are rejected.
- Nobody is contacted. We send nothing to the number or address and never contact the person.
- Anyone can opt out. People can exclude their number or e-mail address through the opt-out form.
- Platform owners can ask for review. The owner of a platform named in our catalog, or someone authorised to act for it, can ask us to review, restrict or remove a check through the Platform Rights Center.
- Customers are responsible. Each customer must have a lawful basis for what it checks and must use results lawfully, under our Terms and Acceptable Use Policy.
- Report abuse to abuse@mobilevalidate.com.
How are phone numbers and e-mails stored?
Identifiers are sealed with public-key encryption as soon as they are stored. The services that take requests can encrypt, but they can't decrypt. Decryption keys are only held by the internal component that has to run the check.
To find repeat checks and apply the suppression list without decrypting anything, we use a keyed blind index. That is a one-way keyed hash of the normalized identifier, and without the secret key it can't be reversed or recomputed. Results are sealed per item as well.
Before anything is stored, phone numbers are normalized to E.164 and e-mail addresses are trimmed and lowercased. This means one identifier maps to exactly one record. Connections to the API and the website use TLS.
Who can see the data?
Almost no one sees full identifiers. Logs, the admin panel, job results and downloads show masked values, such as +44770*****01 for a number or re•••@example.com for an address. We never put phone numbers or e-mail addresses in URLs or request headers, because those end up in access logs. The API only accepts them in request bodies.
API keys are stored as keyed hashes and shown only once, when they are created. You can limit a key to certain scopes, and you can restrict it to your own IP addresses with an allowlist that accepts IPv4 and IPv6 ranges. Unknown, revoked, expired and wrong-IP keys all get the same unauthorized answer, so the error doesn't reveal which case applies. Staff access to the admin panel goes through an identity-aware access gateway and every action is audited.
How long is data kept?
| Data | Default retention |
|---|---|
| Real-time API lookups (identifiers and results) | 7 days |
| Bulk jobs (inputs, results, downloads) | 30 days, configurable per account |
| Per-account check history (sealed), used for your cache and billing evidence | Up to 400 days |
| Operational logs | Masked identifiers only |
You can delete a finished job's data before the retention period ends with DELETE /v1/jobs/{id}. Cached answers live in your account's cache only and are never shared across customers. Billing records keep counts and amounts, not identifiers.
How can people object to being checked?
People whose number or e-mail address may be checked, and people whose number may appear in spam-report data, can use the opt-out form. We review every request. An approved objection puts the identifier on a suppression list, which is checked before every lookup. A suppressed identifier is never checked and shows up in results as suppressed, free of charge. The form's reply is the same in every case, so it never confirms whether we hold data about someone. Requests for access or erasure are handled as described in the data-subject notice.
Which sub-processors do you use?
We use sub-processors in these categories:
- hosting and infrastructure, including network delivery and security
- storage and backups
- e-mail delivery and filtering
- payments
- the AI model provider for the support chat
- data-verification partners that answer individual checks
The named list is given under confidentiality to customers on request, under our data processing agreement. We announce changes at least 14 days in advance, and you can object to them. Partners receive only what a check needs, which is the identifier and the service, and never your account details.
What else protects the service?
- Abuse controls. Requests that look like sequential number ranges or generated e-mail lists are rejected, and each account has a daily cap. See rate limits and abuse.
- No profiling outputs. Checks answer yes, no or unknown, plus defined data fields. We never return names, photos or profiles.
- Signed webhooks. Every delivery is signed and only goes to public HTTPS endpoints that you have verified.
- Cookies. The site uses no analytics or advertising cookies. See the cookie notice.
To report a vulnerability, use the contact in /.well-known/security.txt.
Frequently asked questions
How long do you keep the numbers and e-mails I check?
By default 7 days for API lookups and 30 days for bulk jobs. Your account's job retention can be configured, and you can delete a finished job's data at any time with DELETE /v1/jobs/{id}.
Do other customers benefit from my checks?
No. The cache is per account. A result obtained for your account is never served to another customer.
Who are your sub-processors?
We publish the categories: hosting and infrastructure, storage, e-mail delivery and filtering, payments, the AI model provider for the support chat, and data-verification partners. Customers can get the named list under confidentiality, with 14 days' notice of changes.
Do you use analytics or advertising cookies?
No. The site uses no analytics or advertising cookies. See the cookie notice for the strictly necessary ones.
How do I report a security issue?
Use the contact given in /.well-known/security.txt. Please don't include real personal data in your report.
Do you hold security certifications?
Not at this time. We describe our controls here and don't display certification badges we don't hold.